Cloud-adjacent
Move quickly where public cloud operation is acceptable and target systems permit controlled integration.
Deployment
Cyberm8 can run cloud-adjacent, on-prem, hybrid, or isolated so credentials, topology mappings, and local API keys stay inside the control boundary your environment requires.
Architecture diagram
Cyberm8 can be deployed in the environment your risk model requires: cloud-hosted, customer-hosted, fully isolated, or split across several controlled zones.
Start with a virtual host or cloud provider, place the Cyberm8 where changes are approved, and keep sensitive credentials and topology state inside the right boundary.
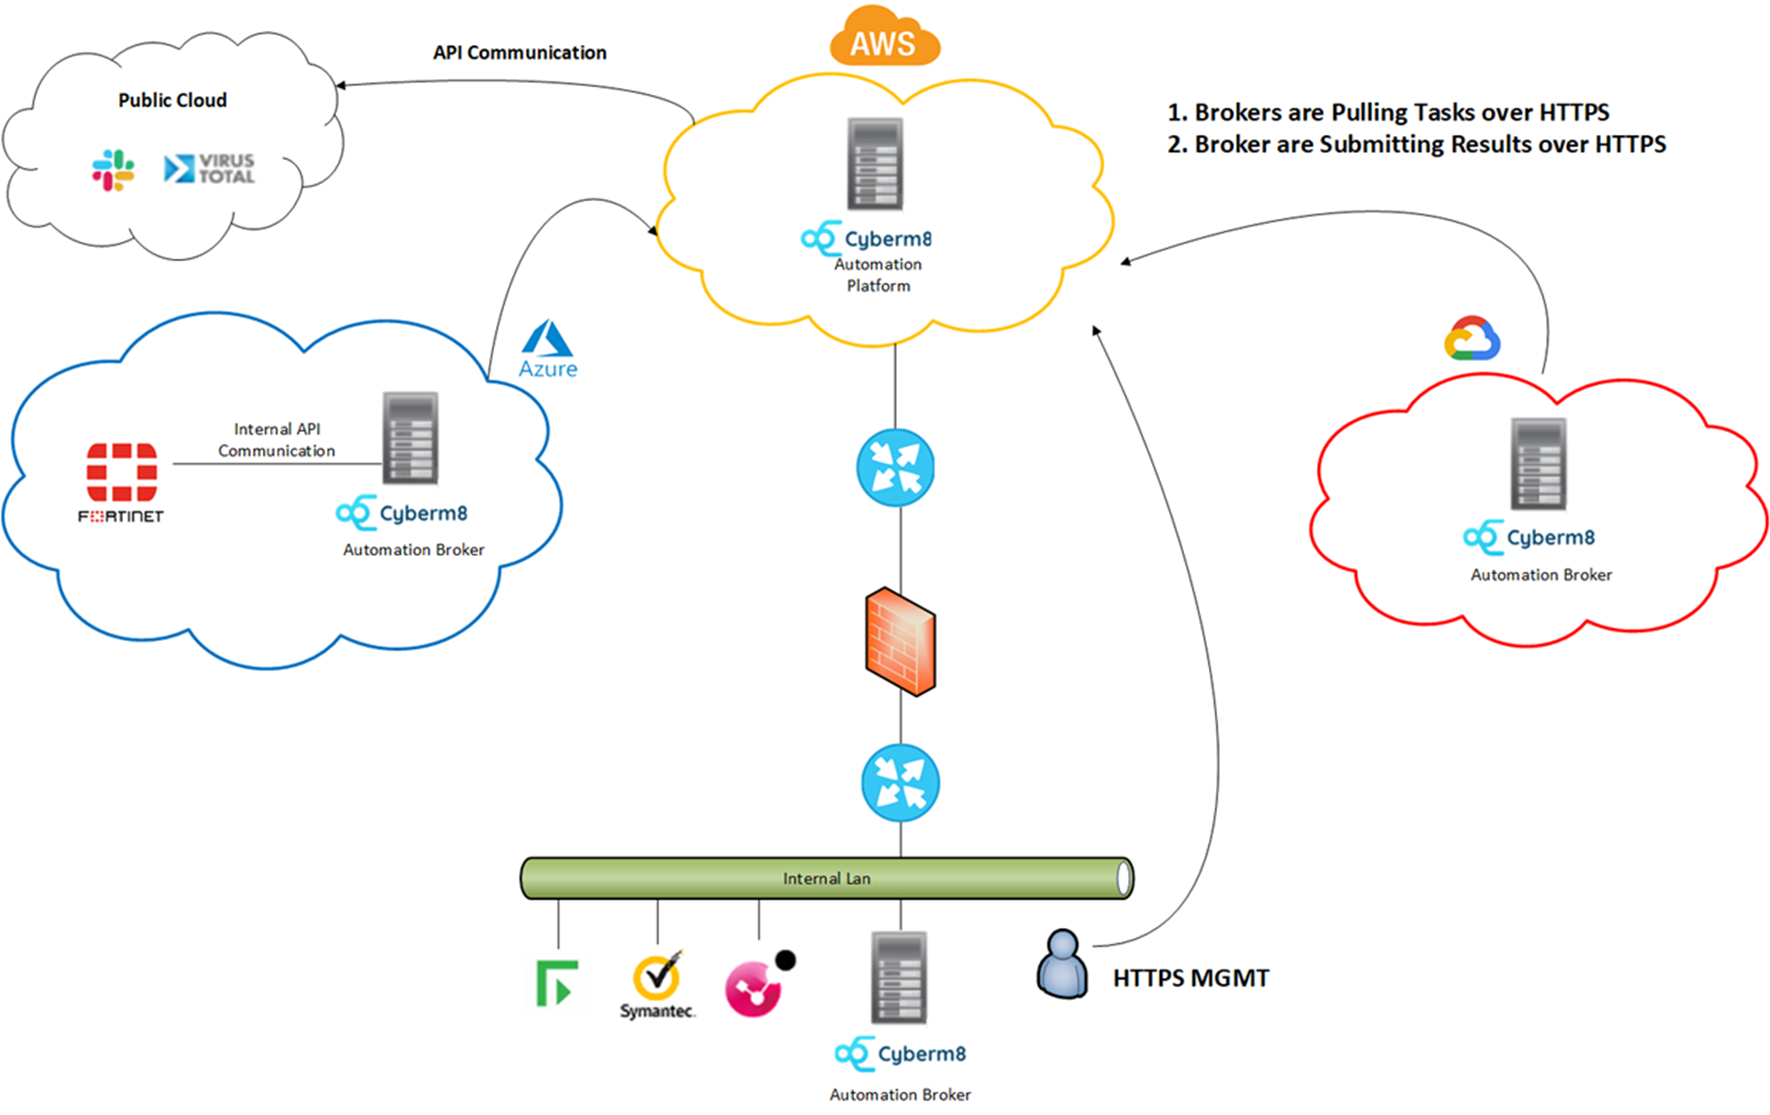
Cyberm8 uses the same workflow model while placing the Cyberm8 where security, residency, and network architecture require changes to happen.
Move quickly where public cloud operation is acceptable and target systems permit controlled integration.
Run the Cyberm8 core inside your own network for local changes and credential control.
Coordinate cloud approved security work with internal action while sensitive actions stay inside local boundaries.
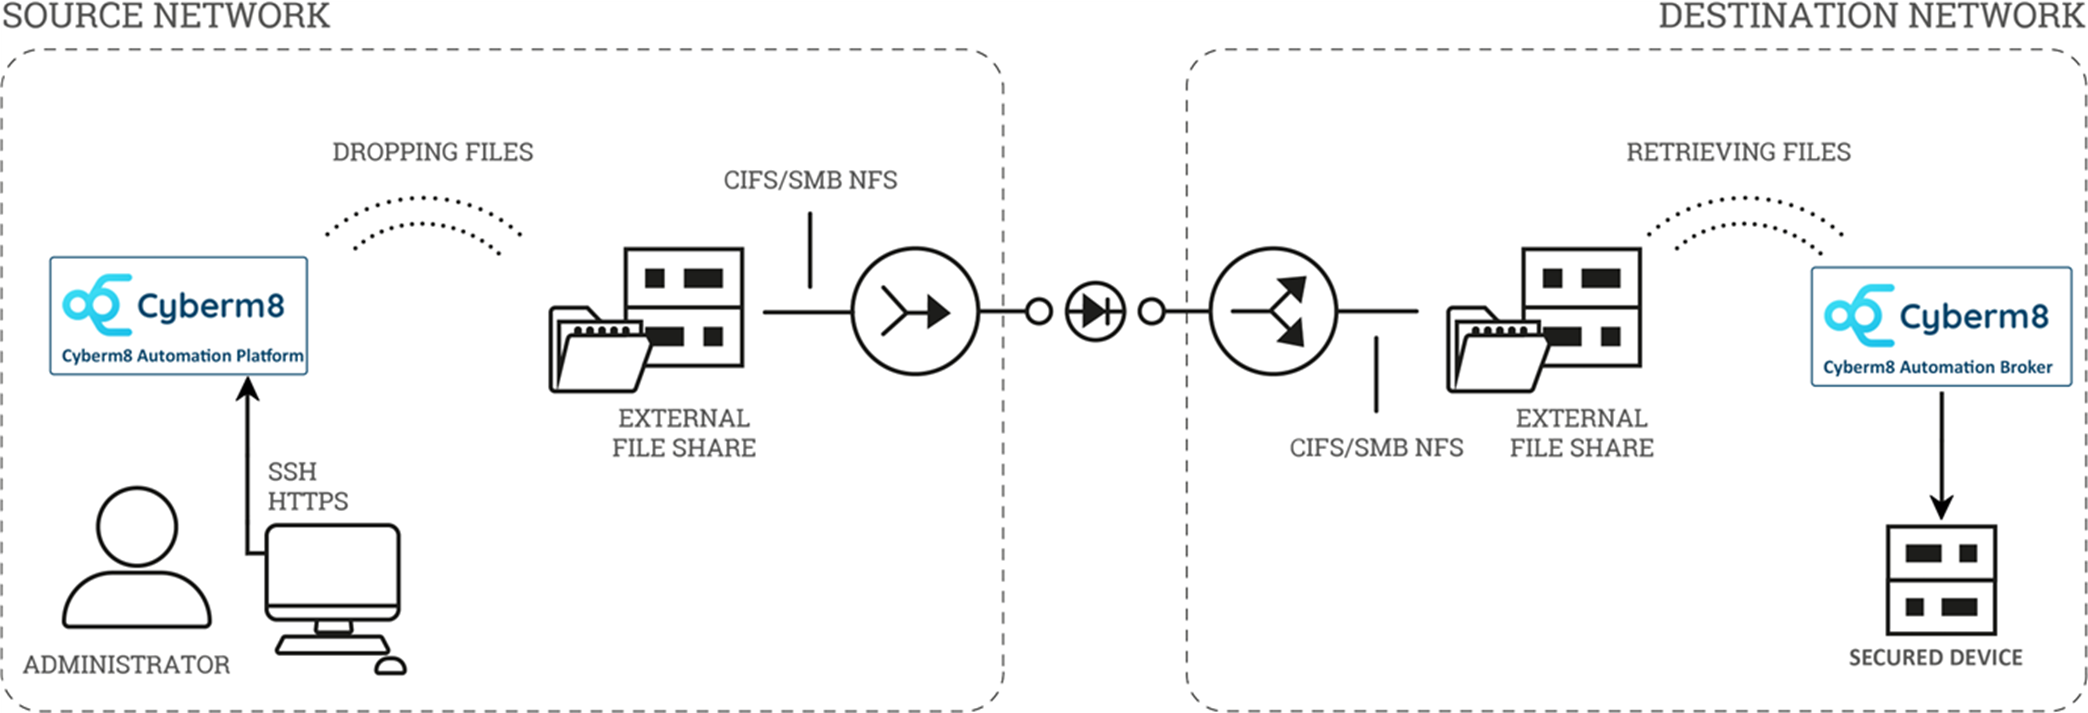
Use a controlled handoff model and controlled transfer patterns for isolated operational networks.
For OT networks behind a diode or controlled transfer path, Cyberm8 can run in the IT environment and send approved commands to an OT-side Cyberm8 component through hot folders.
Your team keeps control over the data path while still running approved work inside the isolated destination network.
Request the deployment specification for Cyberm8 location, network zones, credential handling, and audit design.